Modern security work is less about one magic word and more about choosing the right mechanism for the job. Passkeys, TLS 1.3, hashing, and encryption all live in the same neighborhood, but they solve different problems. If you use the wrong one, the system may still look tidy while quietly doing the wrong thing.
Why this topic matters now
Current guidance is moving in a clear direction: stronger authentication, less password dependence, better token protection, and secure transport by default. OWASP’s terminology guidance separates encoding, hashing, and encryption; its password storage guidance recommends hashing passwords with a modern adaptive algorithm rather than trying to make them reversible. NIST’s consumer guidance now highlights multi-factor authentication and passkeys, and the IETF’s RFC 9852 says new protocols using TLS must require TLS 1.3.
That sounds abstract until you are deciding how to store a password, sign a session token, or send account data across the wire. Then the distinctions matter very quickly.
Encoding vs. hashing vs. encryption
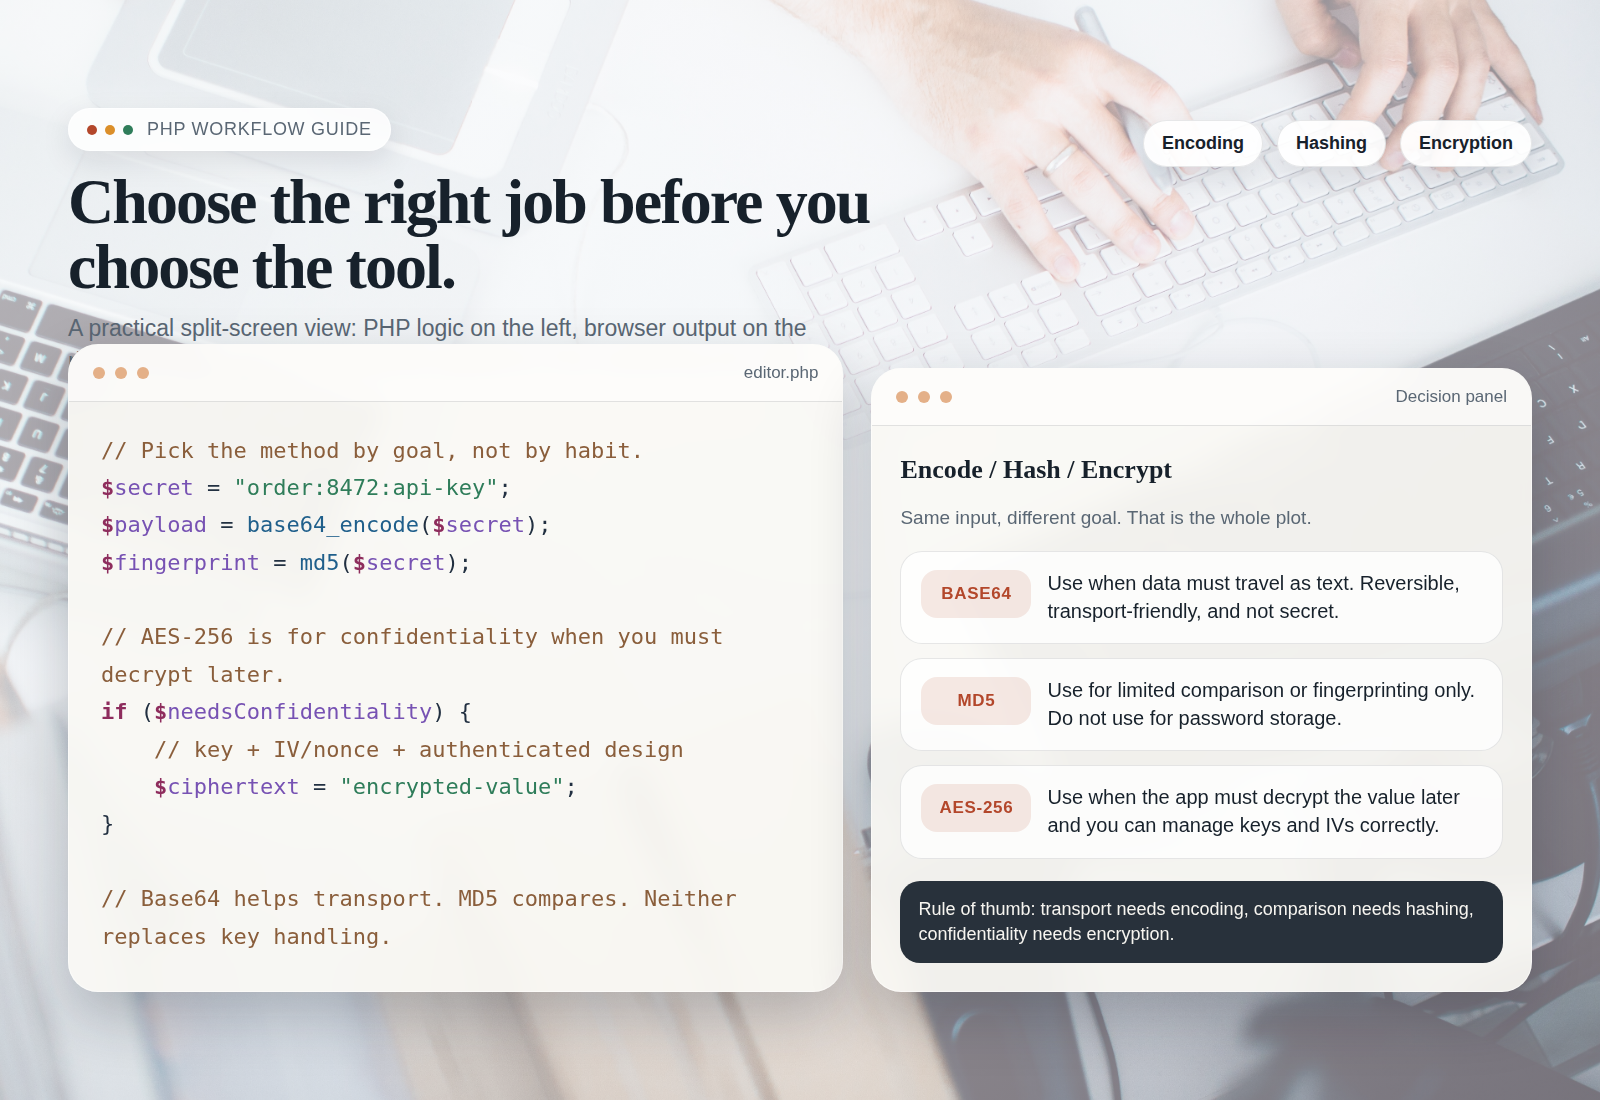
These three words get mixed together constantly, which is how projects inherit expensive confusion.
- Encoding changes representation so data can travel or be displayed correctly. It is not a security control.
- Hashing turns input into a fixed-length digest. It is designed to be one-way for verification, not recovery.
- Encryption protects data so it can be recovered later with the right key.
The practical mistake is to treat any reversible transformation as “security.” If the point is to verify a password, you want hashing. If the point is to protect a secret file or a payload that must be read later, you want encryption. If the point is to make a URL or HTML snippet display safely, you want encoding or escaping.
OWASP’s Security Terminology Cheat Sheet is still one of the cleanest references for keeping those terms straight.
What to use for passwords, tokens, and files
For passwords, the answer is simple: store a salted hash using a modern password hashing function such as Argon2id or bcrypt, depending on your platform and operational constraints. Do not encrypt passwords and call it a day. Reversible password storage is just a future incident with a nicer label.
For session tokens and API secrets, the rule changes. You usually need to preserve the token value for validation, so the right pattern is to protect transport, limit exposure, and store only what you need. Recent NIST guidance emphasizes keeping tokens and assertions protected from misuse, which is a reminder that short-lived, scoped, and well-handled credentials are part of the control surface.
For file storage, encryption makes sense when you need confidentiality at rest. For public links, signed URLs or access controls may be a better fit. For logs, think carefully before storing raw secrets at all. A log line is not a vault just because it is boring.
OWASP’s Password Storage Cheat Sheet lays out the “hash, don’t encrypt” principle in practical terms.
Why TLS 1.3 is now the baseline for new protocols
Transport security is where a lot of teams quietly lose the plot. If your data is protected perfectly at rest but sent over weak transport, you have built a strong lock on a screen door.
TLS 1.3 removes legacy baggage, simplifies negotiation, and gives new protocols a cleaner security baseline. The IETF’s RFC 9852 is direct: new protocols using TLS must require TLS 1.3. That matters for new software design, not just for compliance checklists.
If you are shipping a new application, use TLS 1.3 everywhere you can. If you are maintaining an older system, the migration goal is still obvious: reduce the surface area where older protocol behavior can linger.
For the protocol details, the IETF’s RFC 9852 is the current baseline worth reading directly.
Where passkeys fit
Passkeys change the shape of the login problem. Instead of relying on a password that a user must remember, reuse, and defend from phishing, passkeys use cryptographic keys tied to the device and the relying party. That gives teams a cleaner path away from password-only authentication.
NIST’s current consumer guidance on passwords now points readers toward stronger authentication methods, including multi-factor authentication and passkeys. The practical takeaway is not that passwords disappear overnight. It is that new systems should stop pretending password-only login is the end of the story.
For a useful background reference, the NIST guidance on stronger authentication and passkeys is a good starting point for non-specialists.
A practical checklist for builders
- Use hashing for passwords; never store them with reversible encryption.
- Use encryption for data that must be recovered later and kept confidential at rest.
- Use encoding or escaping for transport/display contexts, not as a security barrier.
- Require TLS 1.3 for new protocols and keep older transport out of the critical path.
- Scope tokens tightly, expire them quickly, and treat them like sensitive credentials.
- Prefer passkeys or other phishing-resistant authentication where supported.
- Make logs, dashboards, and reports useful without exposing secrets you do not need.
Common anti-patterns to avoid
There are a few classics that keep reappearing because they are easy to justify on a whiteboard and painful in production:
- Encoding data and claiming it is protected.
- Using encryption for passwords because it feels more “secure.”
- Leaving old transport settings in place because nothing has broken yet.
- Storing access tokens in places where they can be copied, replayed, or over-logged.
- Adding authentication complexity without reducing phishing risk.
The pattern is the same each time: pick a word that sounds strong, then ignore what the mechanism actually does. Systems are less sentimental than blog posts.
Quick decision guide
| Goal | Best fit | Notes |
|---|---|---|
| Verify a password | Hashing | Use a salted adaptive password hash. |
| Protect a secret file or payload | Encryption | Keep the key handling disciplined. |
| Make text safe for a URL or page | Encoding/escaping | Not a security control by itself. |
| Reduce login phishing risk | Passkeys | Prefer phishing-resistant authentication where possible. |
| Protect data in transit | TLS 1.3 | Baseline for new protocols and modern deployments. |
How this fits the tools on RedKernel-Softwares.com
If you are exploring the site’s tooling, the useful habit is to match the tool to the job instead of forcing every problem through the same lens. The FREEWARES section is a good place to compare utilities, RedKernel Referer Tracker helps you think about source data and reporting, and Sources/Functions… is where small workflow pieces make more sense when used together. For operational visibility, the Reports & Tracking area stays focused on the part that actually matters: seeing what is happening without leaking what should stay private.
Need help getting oriented? The Support page is the right place to start, and the homepage gives the broader picture of the site.
Final takeaway
Choose the method by goal, not by buzzword. Hash passwords. Encrypt recoverable secrets. Encode for transport or display. Use TLS 1.3 for modern transport. Prefer passkeys where they fit. That is the whole game, minus the marketing haze.
If you keep those lines straight, your security design becomes simpler, your review process gets faster, and your systems stop pretending that every sharp-looking term means the same thing.