Quick definitions: what each technique does
If you are choosing between encoding, hashing, and encryption, start with the job you need done rather than the buzzword you remember. The names sound adjacent. The behavior is not.
- Encoding changes data into a different representation so it can travel or fit a format. It is meant to be reversible, and it does not protect secrecy.
- Hashing turns data into a fixed-length digest for verification. It is one-way by design. Good hashing helps you compare values without storing the original.
- Encryption transforms data so only someone with the right key can recover it. It is for confidentiality, not for proving identity or integrity on its own.
That simple distinction is easy to forget when a deadline is nearby. The result is usually a clever-looking mistake.
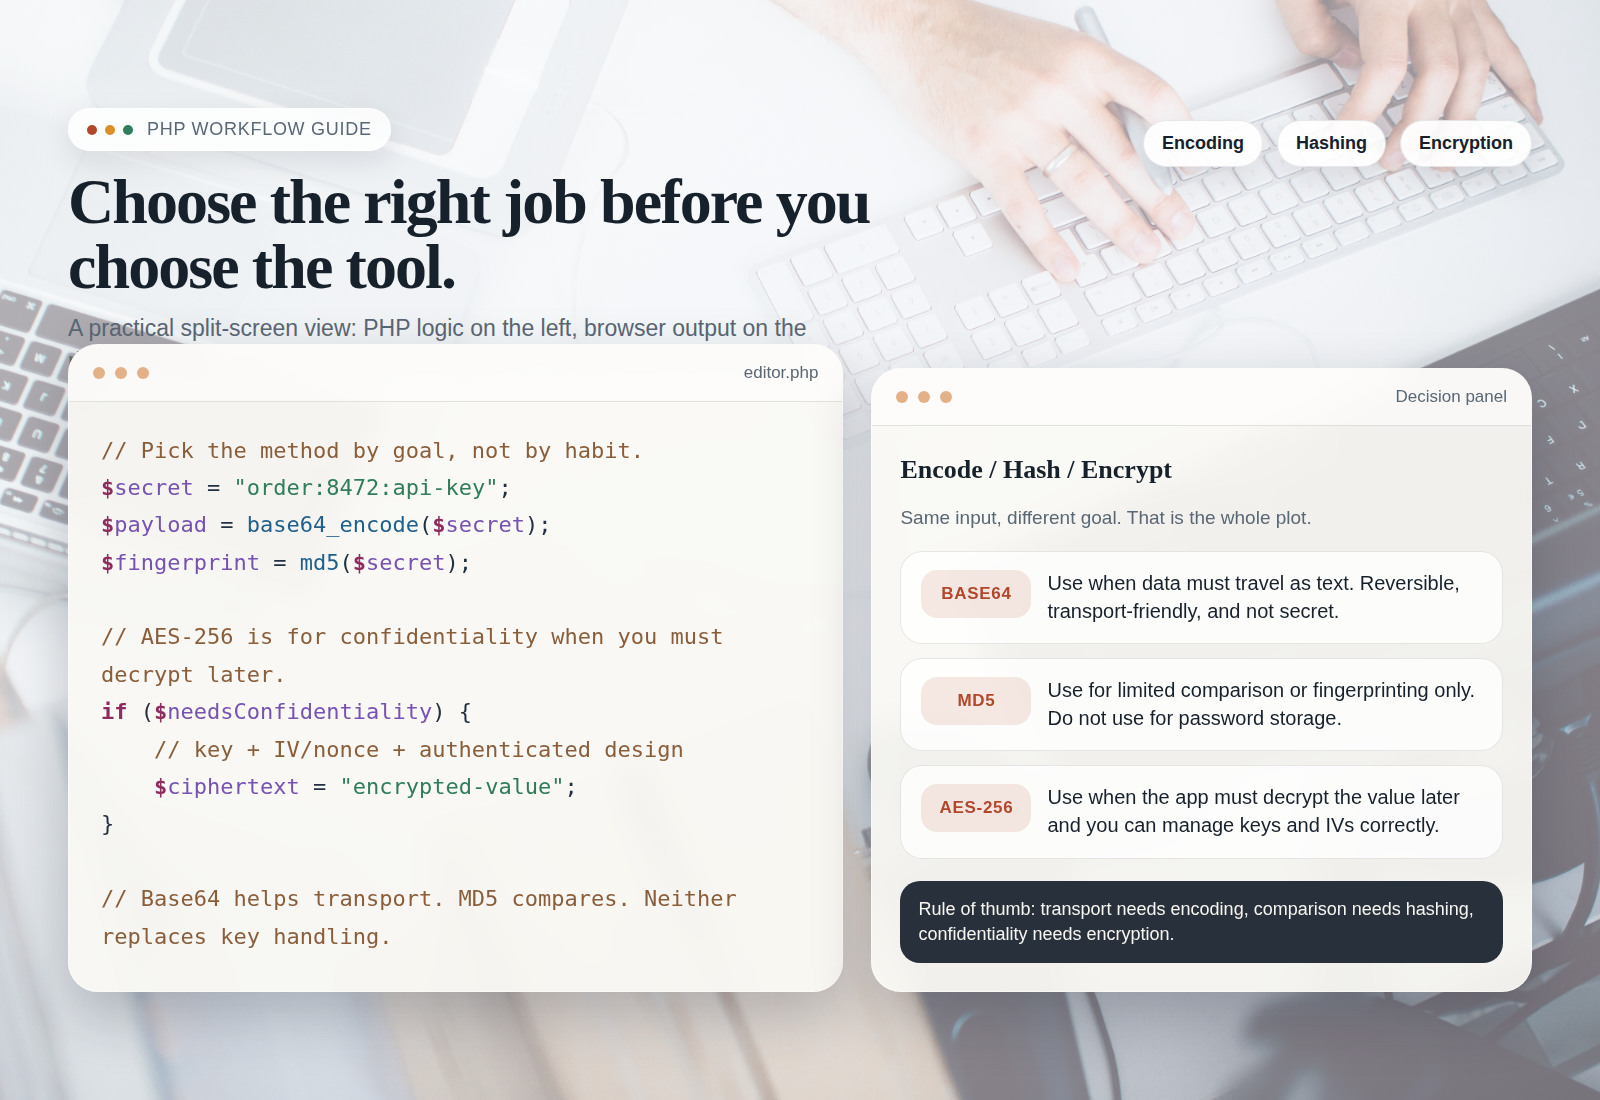
Use-case matrix: choose the tool by the goal
| What you want to achieve | Best fit | Why | What it does not do |
|---|---|---|---|
| Make text safe for a URL, HTML page, or transport format | Encoding | It preserves meaning while adapting the representation | It does not hide the data |
| Verify that data has not changed | Hashing | It gives you a compact fingerprint for comparison | It cannot be reversed into the original value |
| Store a secret so only authorized code can recover it | Encryption | It protects confidentiality with a key | It is not a substitute for password hashing |
For a broader implementation view, the PHP manual pages for base64_encode(), hash(), and the OpenSSL extension are the right starting points. They are not exciting, which is usually a good sign.
For a plain-language baseline on the concepts themselves, hash functions and encoding are worth a quick skim before you build anything that touches secrets.
Common mistakes that cause real problems
- Using hashing for encryption: if you need to recover the original value later, hashing is the wrong tool.
- Using encoding as security: Base64, URL encoding, and HTML entities help with transport or rendering. They do not make data private.
- Using MD5 for passwords: MD5 is fast, which is the opposite of what you want for password storage. Use a modern password hashing API instead.
- Encrypting data that only needs verification: if you only need to check integrity, hashing is simpler and usually easier to manage.
- Storing secrets in plain text because “the app is internal”: internal systems still fail, logs leak, exports happen, and people reuse habits.
PHP already provides a better path for passwords through password_hash() and password_verify(). That is the pattern to reach for when a user needs to log in, not when you need to retrieve the original password. You should not be retrieving it at all.
PHP examples: where each pattern fits
Encoding example: when you build a link parameter, let PHP handle the format conversion.
$query = http_build_query([
    'search' => 'PHP security notes',
    'page'   => 2,
]);
$url = '/reports?' . $query;
Hashing example: when you need an integrity check or a password verifier, use a modern algorithm and a built-in API.
$checksum = hash('sha256', $payload);
// For passwords:
$hash = password_hash($password, PASSWORD_DEFAULT);
Encryption example: when you need to recover the original data later, use authenticated encryption patterns and keep the key outside the database.
$ciphertext = openssl_encrypt(
    $secret,
    'aes-256-cbc',
    $key,
    OPENSSL_RAW_DATA,
    $iv
);
Those snippets are intentionally high level. Production code needs error handling, authenticated modes where available, and a key strategy. There are doors that only open after you stop hard-coding the lock.
Key management basics for encryption
Encryption is only as useful as the key plan behind it. If the key sits next to the ciphertext in the same table, you have mostly built a more complicated way to lose the same data.
- Keep keys out of the database when practical.
- Store them in environment variables, secret managers, or other controlled runtime storage.
- Separate development, staging, and production keys.
- Rotate keys with a documented migration path for existing ciphertext.
- Never log raw keys, recovery tokens, or decrypted values unless you have a very strong reason and a very small audience.
For practical server-side guidance, the OWASP Cryptographic Storage Cheat Sheet is a useful reference point. It is not a shortcut, but it is a good map.
What to store in databases
| Data type | Store as | Suggested field name | Notes |
|---|---|---|---|
| User password | Hash | password_hash | Never store the original password |
| API secret or private token | Encrypted ciphertext | api_secret_encrypted | Protect the key separately |
| URL-safe or HTML-safe text | Plain text or encoded at output time | display_name, query_value | Encode for the context where you render it |
| Integrity checksum | Hash | payload_checksum | Use it to compare, not to conceal |
Clear field names matter. They keep future maintainers from guessing whether a column holds plain text, a digest, or ciphertext. Guessing is not a storage strategy.
FAQ
Should I encrypt referer data?
Usually no, not by default. For most analytics or reporting use-cases, the right question is how much referer information you really need, whether you should store it at all, and how long it should stay in the system. If you are collecting source data, our Reports & Tracking and Sources/Functions… pages are the better places to think about data scope before you think about secrecy.
Should I encrypt URLs?
Usually no. If the goal is to make a URL safe for transport, use URL encoding. If the goal is to hide sensitive query data, the better answer is often not to put that data in the URL in the first place. URLs leak through logs, referrers, browser history, and screenshots more often than teams expect.
What about Base64 in transit?
Base64 is not encryption. It is a way to represent binary or structured data in a text-friendly form. It can be useful in transit or storage formats, but it offers no secrecy. If you need a practical primer on data handling in a broader workflow, see the Support page for the clearest next step.
A 5-step decision flow you can reuse
- Do I need to recover the original value later? If no, hashing may be enough. If yes, consider encryption.
- Am I only changing the format? If yes, encode for the destination context.
- Am I trying to prove something has not changed? If yes, hash it.
- Am I trying to hide confidential data? If yes, encrypt it and plan the keys.
- Will this value live in logs, URLs, or database fields? Label it clearly and store the minimum needed.
If you keep that sequence in mind, the choice usually becomes plain. Not all victories are dramatic; some are just avoiding the wrong primitive in the first place.
For more practical context, the home page, blog, and the related Sources/Functions… and Reports & Tracking pages make a useful path through the site’s developer workflow.